A Git update is incomplete until every bundled copy is checked
A patched terminal is only one part of a Git update. Check the copies inside development tools and build environments, then verify which version each workflow actually runs.
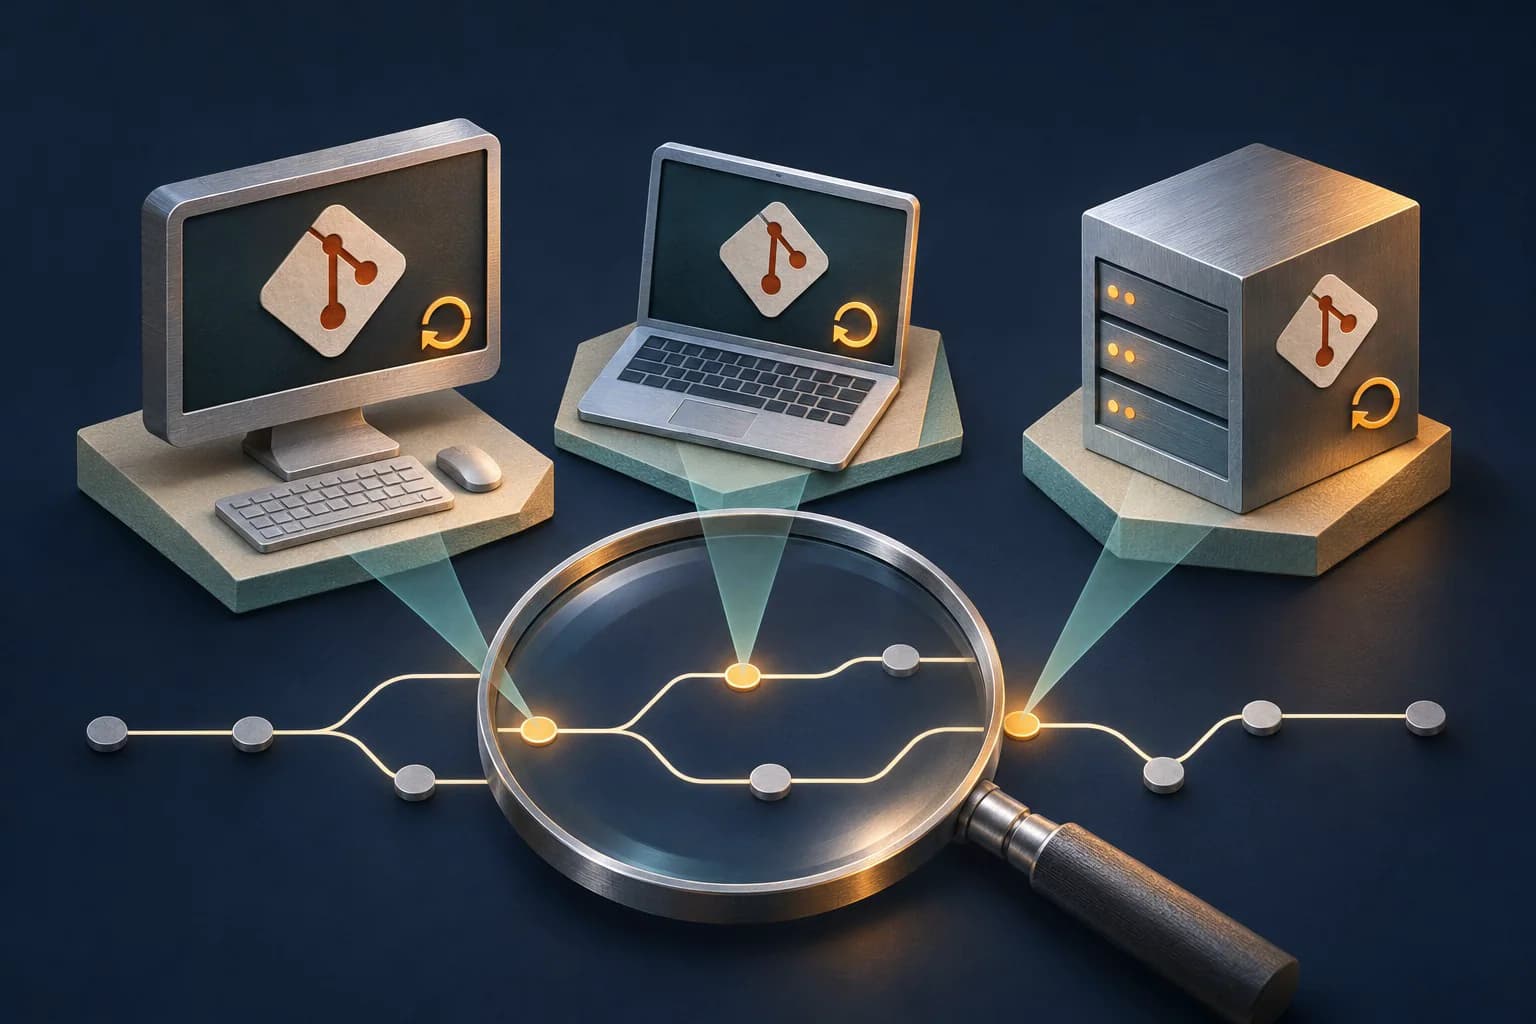
You update Git in a terminal, check the version, and return to work. That is a useful start. It does not tell you what a desktop client, an IDE, or a build worker will use when it opens a repository.
The November 10 Git security release makes that distinction worth checking. Git 2.56.1 and patched maintenance releases address six vulnerabilities. One concerns a recursive clone: copying a repository together with its submodules, the other repositories it references.
Why the clone operation deserves attention
CVE-2026-111760 can allow a malicious repository to cause code execution during a recursive clone. The Git advisory describes an attacker-controlled server and a crafted repository that redirects a submodule's metadata to malicious configuration or hooks. This is not a claim that every ordinary clone executes untrusted code, nor evidence that your repositories have been attacked.
The GitHub announcement recommends updating Git and applications that bundle their own copy. The release notes confirm fixes in 2.56.1 and the corresponding maintenance releases: 2.55.1, 2.54.1, 2.53.1, 2.52.1, 2.51.3, and 2.50.2. Check your distributor's advisory as well; a supported package may carry a backported fix without adopting the newest upstream version number.
Make the inventory match the work
For each place that handles repositories, record the executable actually used and who updates it. Start with a developer terminal, then check graphical clients and IDE integrations. For automation, include the worker image and any container image that brings its own tools.
| Where Git runs | What to verify |
|---|---|
| Terminal | Executable path, version, and package supplier |
| Desktop client or IDE | Whether it uses system Git or a bundled copy |
| Build worker | The Git inside the image actually deployed to the job |
This table is a practical inventory method, not a claim that every listed product is affected. Keep a separate result for each installation. A successful update in one row should not close the others automatically.
While an update is pending
Do not recursively clone repositories from sources you do not trust. For the other issues covered by this release, GitHub also advises avoiding untrusted merges, tags, binary patches, and fast-import streams while updates are pending. These precautions reduce exposure; they do not replace the fixes.
After deployment, repeat the version and executable checks in the environment that runs the real job. Save the package advisory or release evidence with your inventory. The useful completion criterion is a verified result for each Git installation, rather than a single green update notification.
Anna
Digital safety and consumer research editor at Internet AnalysisAnna edits practical guides to safer internet use, privacy and online services. She helps readers understand everyday risks and choose sensible actions without alarmism or blame.
View author profile →How this article was prepared
She checks claims against reliable sources, removes unsupported certainty and separates general information from professional advice. Her short, direct explanations distinguish prevention from the steps needed after an incident.
Read our methodology →Reviewed by the Internet Analysis Editorial Team
Reviewed by the Internet Analysis Editorial Team · Updated November 12, 2026
Meet the editorial team →Article context, review and related questions
A patched terminal is only one part of a Git update. Check the copies inside development tools and build environments, then verify which version each workflow actually runs.
| Measure | Value | Context |
|---|---|---|
| Article type | security | Editorial classification |
| Reading time | 2 minutes | Estimated at approximately 220 words per minute |
| Editorial review | Internet Analysis Editorial Team | Updated November 12, 2026 |
| Review date | November 12, 2026 | Latest stored article update |
Methodology
She checks claims against reliable sources, removes unsupported certainty and separates general information from professional advice. Her short, direct explanations distinguish prevention from the steps needed after an incident.
Full methodology →Data freshness
- Page updated
- Data period
- November 12, 2026
- Responsible editor
- AnnaDigital safety and consumer research editor
Primary sources
- Internet Analysis editorial methodologyReview and limitation rules
Limitations
- The article is informational and may simplify technical details for readability.
- Products, standards, prices and service availability can change after the review date.
- The latest review date does not guarantee that every external product or service remains unchanged.
Related questions
What is the main point of “A Git update is incomplete until every bundled copy is checked”?
A patched terminal is only one part of a Git update. Check the copies inside development tools and build environments, then verify which version each workflow actually runs.
How was this article prepared?
She checks claims against reliable sources, removes unsupported certainty and separates general information from professional advice. Her short, direct explanations distinguish prevention from the steps needed after an incident.
When was this information last reviewed?
The latest stored review or update date is November 12, 2026.