The admin console beside your login deserves its own security review
A practical security review for identity-management consoles: separate authentication, deliberate access controls and release checks that survive deployment changes.
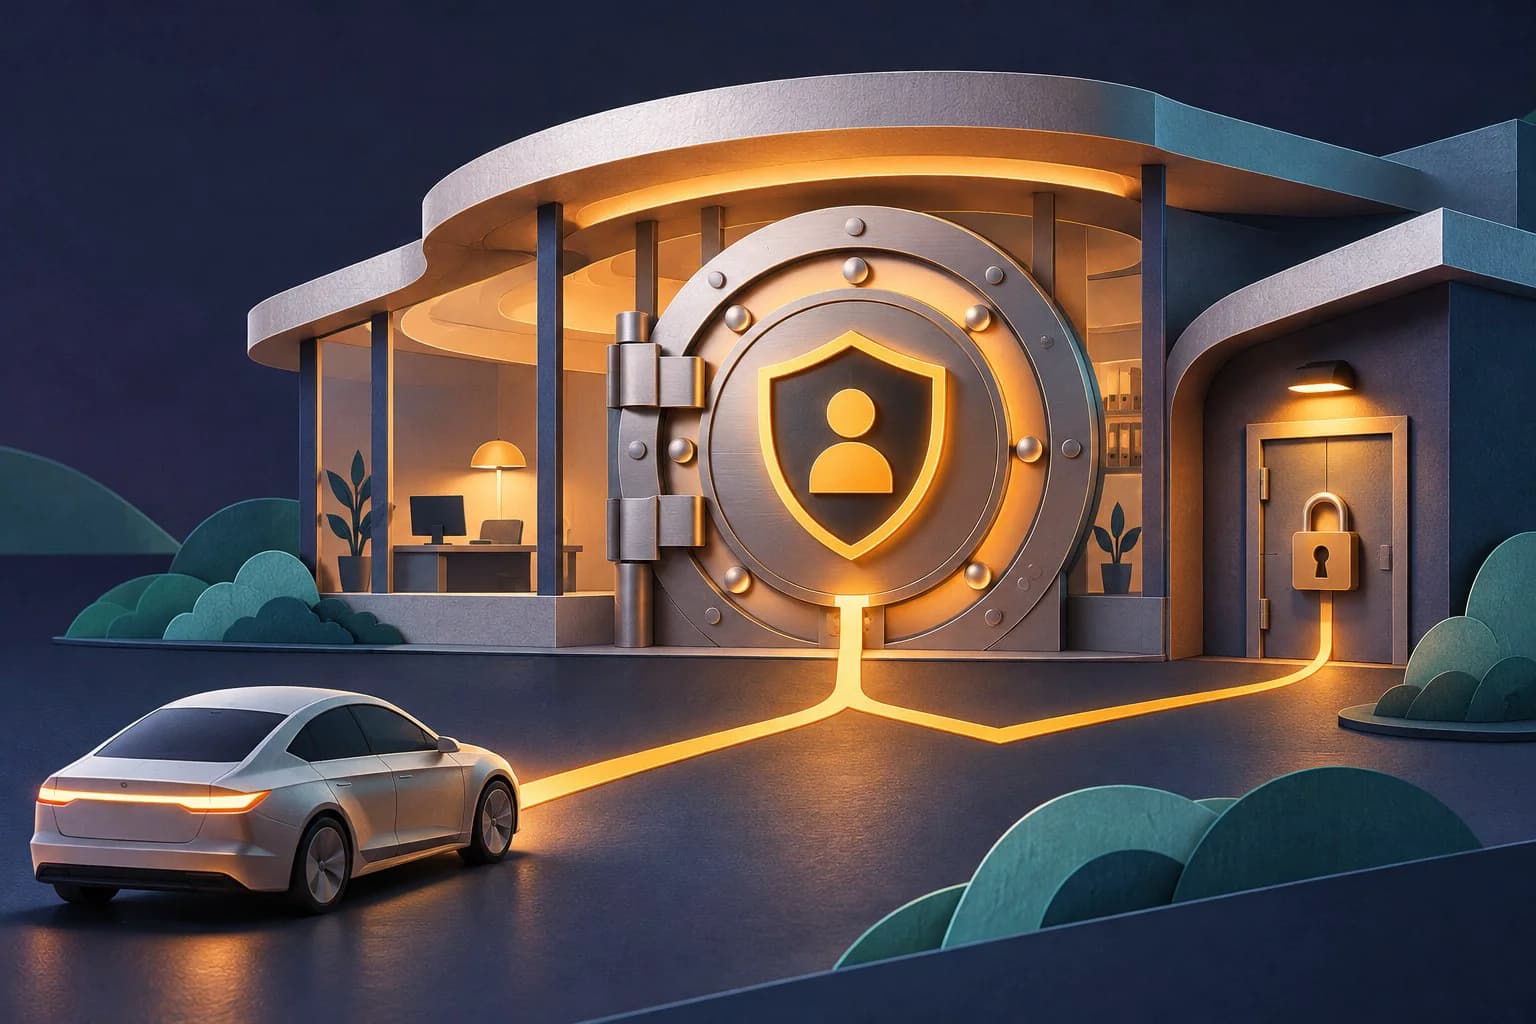
A customer login page may be carefully secured while an administration console beside it still accepts its installation password. For teams responsible for identity systems, the useful question is not just whether customers can sign in safely. It is who can change the records and configuration behind that sign-in.
A connected-car case with a wider lesson
In research published on November 7, Shubham Shah and Sam Curry described a chain affecting the login infrastructure of two unnamed automakers. The edge security layer and the application interpreted request paths differently, letting the researchers reach an administrative console that retained default credentials.
Control of that console led to execution on the identity server and changes to customer records. The researchers then obtained normal app access, including supported vehicle commands. They say the complete chain was tested only with US accounts and vehicles they owned or had permission to use. Both automakers fixed the reported issue within about two hours. This is a disclosed, remediated case, not evidence that every connected car or every deployment of the identity software is vulnerable.
Check the console as a separate entrance
PingIDM's production-hardening documentation says to remove or protect development and debugging tools. It specifically identifies the Felix web console and explains that its authentication is separate from IDM authentication. Securing the customer-facing login therefore does not establish that this console has been secured.
For deployments using this component, follow the instructions for the installed version. If the console is unnecessary, the documented removal procedure covers its bundle, associated plugins and configuration file. If it must remain, replace the default console credentials using the supported configuration mechanism. Record who owns that decision and how it will be checked after deployment changes.
Turn a hardening task into a verifiable result
| Review question | Evidence to retain |
|---|---|
| Which administrative tools are installed? | A component inventory and an owner for each retained console. |
| What protects each entrance? | Its own authentication configuration and approved network-access policy. |
| Do edge and backend controls agree? | Results from authorized tests covering the deployed routing stack. |
| Will the decision survive a change? | A release check that detects reintroduced tools or default settings. |
The table is an operational review framework, not a vulnerability detector. A blocked request proves what happened to that request through that route; it does not establish that every equivalent route is blocked. Scope testing to systems you are authorized to assess, and retain enough configuration context to reproduce the result safely.
The practical goal is a deployment where every administrative entrance has an explicit purpose, an owner and independently verified protection. A successful customer login is only one part of that review.
Anna
Digital safety and consumer research editor at Internet AnalysisAnna edits practical guides to safer internet use, privacy and online services. She helps readers understand everyday risks and choose sensible actions without alarmism or blame.
View author profile →How this article was prepared
She checks claims against reliable sources, removes unsupported certainty and separates general information from professional advice. Her short, direct explanations distinguish prevention from the steps needed after an incident.
Read our methodology →Reviewed by the Internet Analysis Editorial Team
Reviewed by the Internet Analysis Editorial Team · Updated November 9, 2026
Meet the editorial team →Article context, review and related questions
A practical security review for identity-management consoles: separate authentication, deliberate access controls and release checks that survive deployment changes.
| Measure | Value | Context |
|---|---|---|
| Article type | security | Editorial classification |
| Reading time | 2 minutes | Estimated at approximately 220 words per minute |
| Editorial review | Internet Analysis Editorial Team | Updated November 9, 2026 |
| Review date | November 9, 2026 | Latest stored article update |
Methodology
She checks claims against reliable sources, removes unsupported certainty and separates general information from professional advice. Her short, direct explanations distinguish prevention from the steps needed after an incident.
Full methodology →Data freshness
- Page updated
- Data period
- November 9, 2026
- Responsible editor
- AnnaDigital safety and consumer research editor
Primary sources
- Internet Analysis editorial methodologyReview and limitation rules
Limitations
- The article is informational and may simplify technical details for readability.
- Products, standards, prices and service availability can change after the review date.
- The latest review date does not guarantee that every external product or service remains unchanged.
Related questions
What is the main point of “The admin console beside your login deserves its own security review”?
A practical security review for identity-management consoles: separate authentication, deliberate access controls and release checks that survive deployment changes.
How was this article prepared?
She checks claims against reliable sources, removes unsupported certainty and separates general information from professional advice. Her short, direct explanations distinguish prevention from the steps needed after an incident.
When was this information last reviewed?
The latest stored review or update date is November 9, 2026.