PapRAT: review what runs behind an unexpected Windows attachment
A defensive review of suspicious Windows attachments: connect process activity, installers, scheduled tasks and network events before deciding what happened.
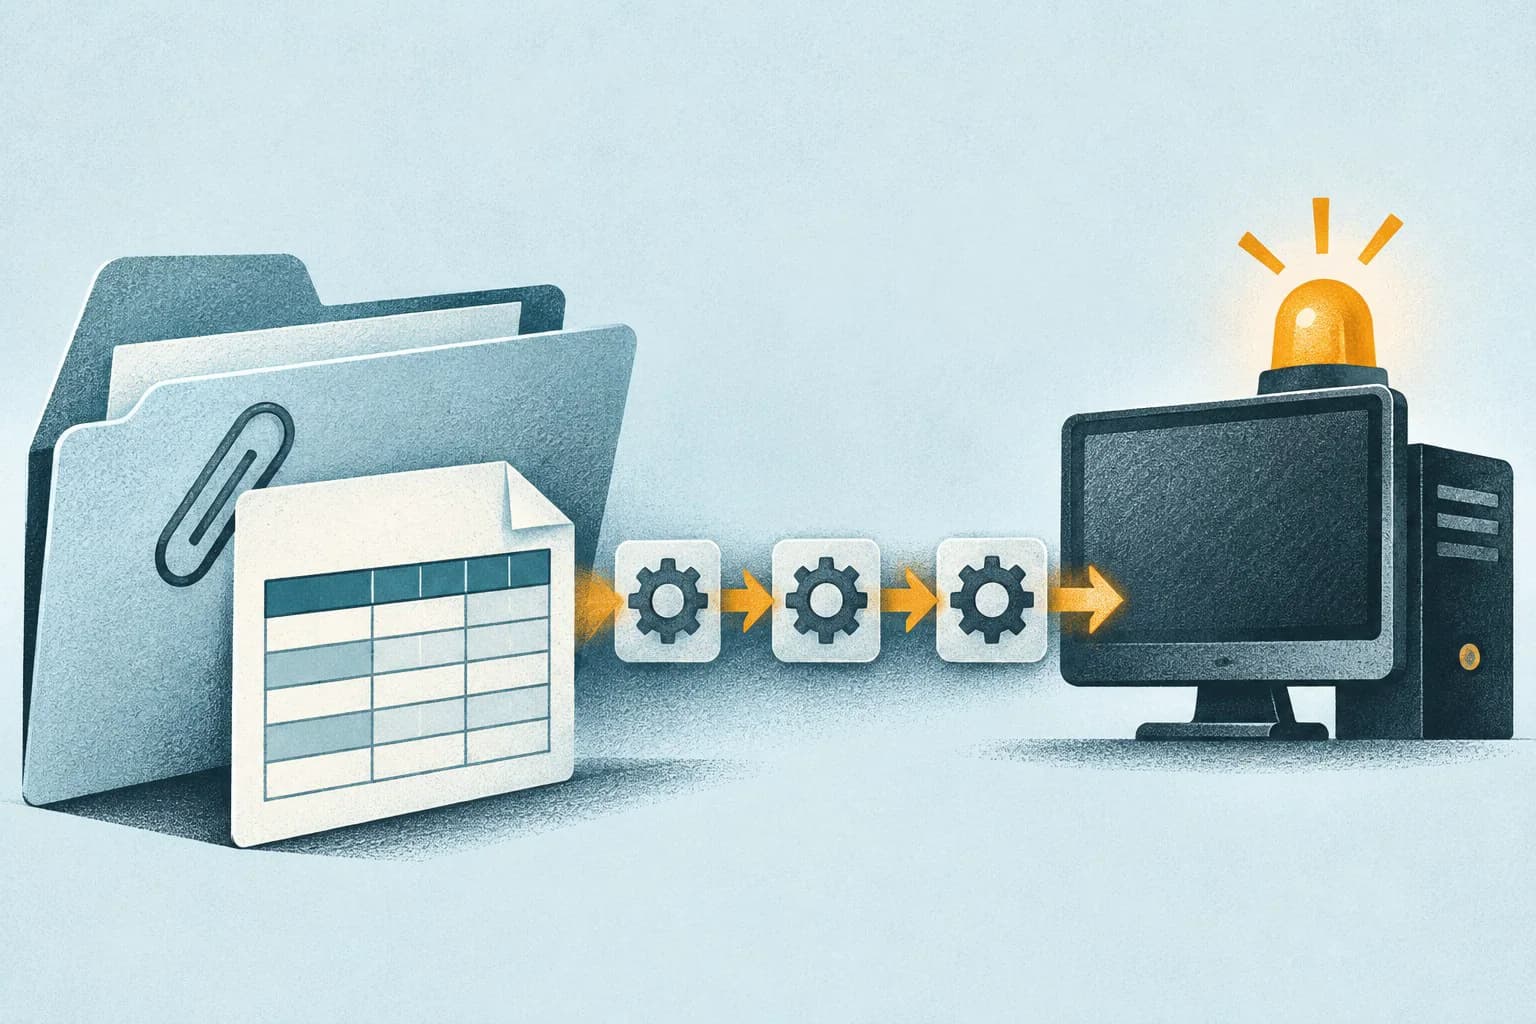
A spreadsheet opening successfully does not tell you what else its launcher started. For a Windows security team, the useful question is what ran around that document: which process created it, what it launched, and whether it left a task behind.
The campaign behind the warning
A November 2 FortiGuard Labs report describes activity attributed with high confidence to BITTER, targeting organizations in South Asia. The researchers observed three delivery paths involving Windows shortcuts, disk images, scripts and installers. Two paths deployed PapRAT; one used native tools and scripts without a conventional malware executable. A decoy spreadsheet could open while an installer ran in the background.
PapRAT supports remote commands, file transfer and screenshots. The report describes C++ and Rust variants. These findings concern a documented espionage campaign; they do not establish that every unexpected shortcut is PapRAT or that an organization elsewhere has been compromised.
Review the sequence, not just the filename
For triage, build a short timeline linking the attachment or download to process creation, installer activity, scheduled tasks and outbound connections. Ask whether that sequence fits an approved business workflow. A familiar executable name is context, not a verdict.
| Review question | Evidence to collect |
|---|---|
| What actually opened? | The original file, its type and delivery context. |
| What ran with it? | Parent and child processes, timestamps and available command-line telemetry. |
| What persisted? | New or modified scheduled tasks and their configured actions. |
| Where did it connect? | Destination history correlated with the same host and time. |
This is a review framework, not a campaign-specific detector. Legitimate administration can produce individual events in the table. Escalate on the combined evidence, preserve it, and follow your incident-response process rather than opening a suspect file again to see what happens.
Test prevention without breaking normal work
Microsoft Defender attack surface reduction includes rules aimed at executable content arriving through email and risky application behavior. Check each rule's prerequisites, exclusions and documented scope. Pilot suitable rules in audit mode before broad enforcement; a rule's name is not proof that it blocks every shortcut or disk-image route.
Give staff a simple alternative when an unexpected attachment requests extra steps: stop and verify the request through a known contact channel. For administrators, pair that habit with visibility into execution and persistence. The objective is a traceable decision about suspicious activity, not a promise that one file filter or one product stops every attack.
Anna
Digital safety and consumer research editor at Internet AnalysisAnna edits practical guides to safer internet use, privacy and online services. She helps readers understand everyday risks and choose sensible actions without alarmism or blame.
View author profile →How this article was prepared
She checks claims against reliable sources, removes unsupported certainty and separates general information from professional advice. Her short, direct explanations distinguish prevention from the steps needed after an incident.
Read our methodology →Reviewed by the Internet Analysis Editorial Team
Reviewed by the Internet Analysis Editorial Team · Updated November 9, 2026
Meet the editorial team →Article context, review and related questions
A defensive review of suspicious Windows attachments: connect process activity, installers, scheduled tasks and network events before deciding what happened.
| Measure | Value | Context |
|---|---|---|
| Article type | security | Editorial classification |
| Reading time | 2 minutes | Estimated at approximately 220 words per minute |
| Editorial review | Internet Analysis Editorial Team | Updated November 9, 2026 |
| Review date | November 9, 2026 | Latest stored article update |
Methodology
She checks claims against reliable sources, removes unsupported certainty and separates general information from professional advice. Her short, direct explanations distinguish prevention from the steps needed after an incident.
Full methodology →Data freshness
- Page updated
- Data period
- November 9, 2026
- Responsible editor
- AnnaDigital safety and consumer research editor
Primary sources
- Internet Analysis editorial methodologyReview and limitation rules
Limitations
- The article is informational and may simplify technical details for readability.
- Products, standards, prices and service availability can change after the review date.
- The latest review date does not guarantee that every external product or service remains unchanged.
Related questions
What is the main point of “PapRAT: review what runs behind an unexpected Windows attachment”?
A defensive review of suspicious Windows attachments: connect process activity, installers, scheduled tasks and network events before deciding what happened.
How was this article prepared?
She checks claims against reliable sources, removes unsupported certainty and separates general information from professional advice. Her short, direct explanations distinguish prevention from the steps needed after an incident.
When was this information last reviewed?
The latest stored review or update date is November 9, 2026.