Phishing: pause, verify and know what to do next
Learn a repeatable way to check suspicious messages, plus the different actions to take after opening a link or sharing a password.
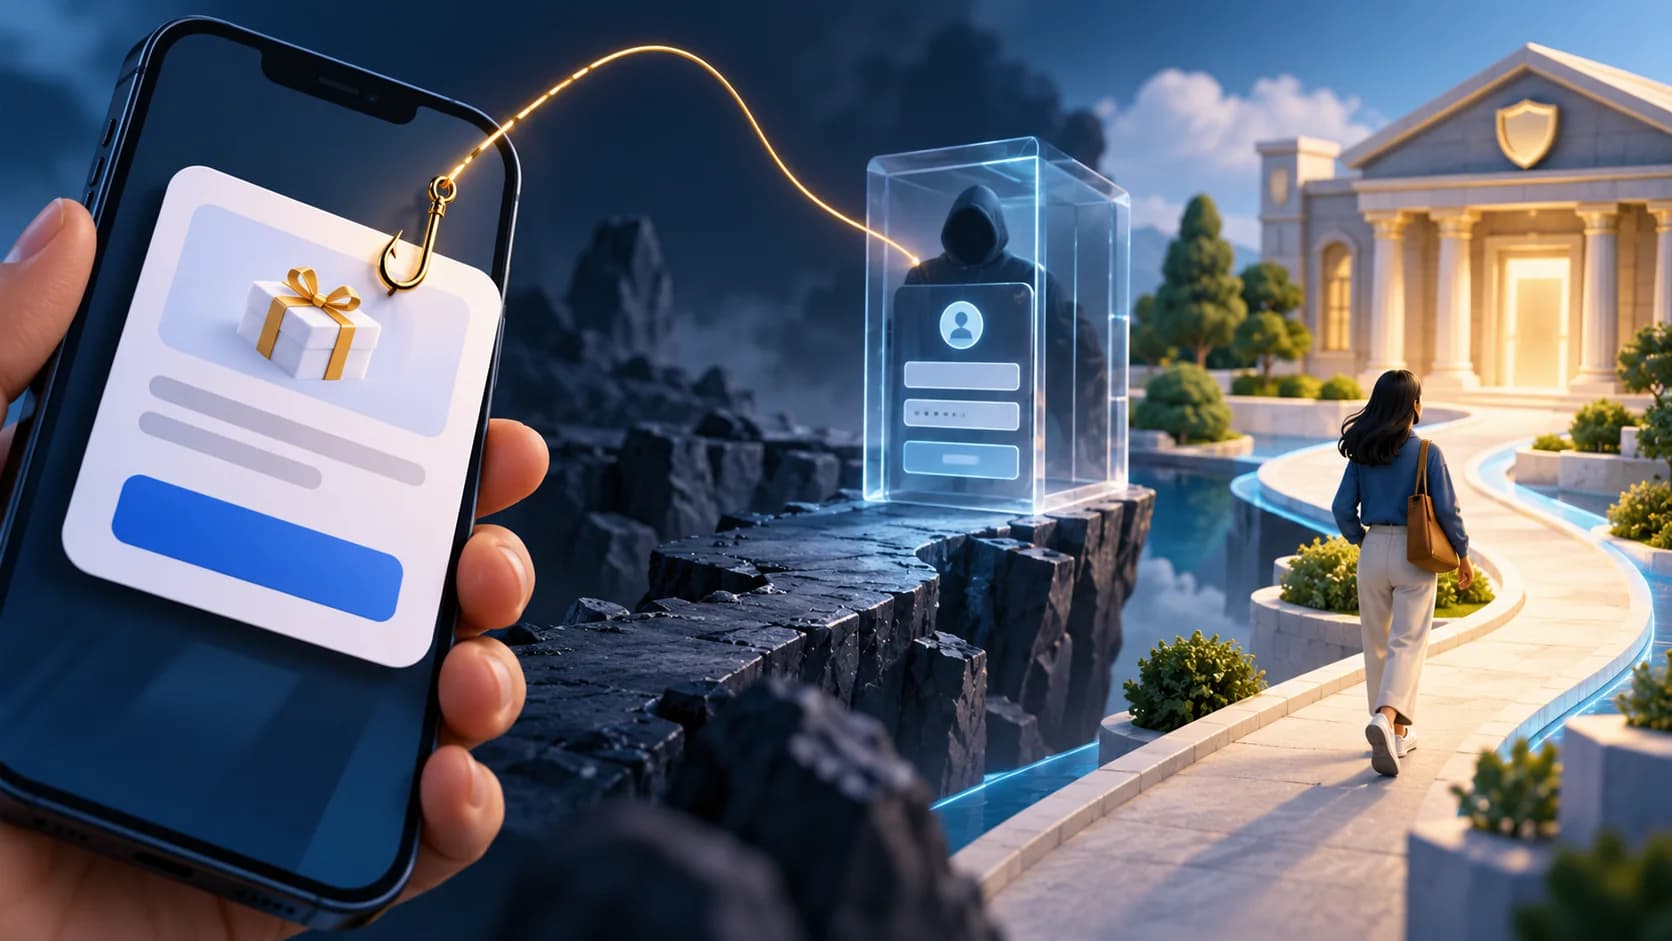
A message says a small payment is missing and your parcel will be returned today. The amount looks harmless. Before paying, open the delivery company's app yourself and check the shipment there. That short pause breaks the path the sender wants you to follow.
Verify the request in the real app or through a known contact, not through the shortcut supplied in the message.
Look at the requested action
Phishing uses a misleading identity or story to obtain information, money or access. It can arrive by email, text, a chat message, a QR code or a phone call. The useful question is what the sender wants you to do, not whether the message looks polished.
Urgency, unexpected login requests, changes to bank details and requests to install software deserve an independent check. Poor grammar can be a clue, but accurate language, a familiar display name and a convincing logo do not establish authenticity.

Verify through a route you choose
- Stop using the link, attachment or telephone number supplied in the message.
- Open the organisation's usual app, a saved bookmark or a known address.
- Check whether the request exists in your account. For a payment or account change, confirm through a previously known contact.
- If the request is not genuine, report it using your service's reporting tools or the relevant incident-response channel, then remove it.
A padlock or HTTPS means that a connection is encrypted. A criminal can operate an encrypted website too. Read the actual domain; a company name elsewhere in the address is not enough. On a small screen, do not rush past truncated addresses.
Respond to what actually happened
| What happened | Immediate response |
|---|---|
| You only received the message | Do not interact; verify and report |
| You opened the page but entered nothing | Close it, check downloads and keep the browser updated |
| You submitted a password | Change it on the real site, end other sessions and review account activity |
| You shared payment details or sent money | Contact the bank or payment provider promptly through a trusted channel |
| You installed software or granted remote access | Stop the remote session, disconnect the affected device from the network and seek trusted technical help |
Opening a link does not always mean the device has been infected, and entering a password can cause harm without installing anything. Match the response to the exposure. If a work account or device is involved, notify the security team promptly rather than trying to hide the mistake.
Make the next attempt harder
Use unique passwords and enable multifactor authentication. Where supported, passkeys or security keys provide phishing-resistant sign-in. A password manager that refuses to fill a familiar login on an unexpected domain is a reason to check the address, not to bypass the warning.
Recovery deserves attention too. Review the email address and phone number used to recover important accounts. Someone with control of that route may be able to undo a password change. Getting help early is more useful than blaming yourself for a message designed to mislead.
Anna
Digital safety and consumer research editor at Internet AnalysisAnna edits practical guides to safer internet use, privacy and online services. She helps readers understand everyday risks and choose sensible actions without alarmism or blame.
View author profile →How this article was prepared
She checks claims against reliable sources, removes unsupported certainty and separates general information from professional advice. Her short, direct explanations distinguish prevention from the steps needed after an incident.
Read our methodology →Reviewed by the Internet Analysis Editorial Team
Reviewed by the Internet Analysis Editorial Team · Updated October 28, 2026
Meet the editorial team →Article context, review and related questions
Learn a repeatable way to check suspicious messages, plus the different actions to take after opening a link or sharing a password.
| Measure | Value | Context |
|---|---|---|
| Article type | Digital security | Editorial classification |
| Reading time | 3 minutes | Estimated at approximately 220 words per minute |
| Editorial review | Internet Analysis Editorial Team | Updated October 28, 2026 |
| Review date | October 28, 2026 | Latest stored article update |
Methodology
She checks claims against reliable sources, removes unsupported certainty and separates general information from professional advice. Her short, direct explanations distinguish prevention from the steps needed after an incident.
Full methodology →Data freshness
- Page updated
- Data period
- October 28, 2026
- Responsible editor
- AnnaDigital safety and consumer research editor
Primary sources
- Internet Analysis editorial methodologyReview and limitation rules
Limitations
- The article is informational and may simplify technical details for readability.
- Products, standards, prices and service availability can change after the review date.
- The latest review date does not guarantee that every external product or service remains unchanged.
Related questions
What is the main point of “Phishing: pause, verify and know what to do next”?
Learn a repeatable way to check suspicious messages, plus the different actions to take after opening a link or sharing a password.
How was this article prepared?
She checks claims against reliable sources, removes unsupported certainty and separates general information from professional advice. Her short, direct explanations distinguish prevention from the steps needed after an incident.
When was this information last reviewed?
The latest stored review or update date is October 28, 2026.